ChangeLogs
Specifically made to address my forgetfulness by a bit, basically a more organized version of the journals. Note: the date written for update before June/2026 are estimated date +1 to 10 days
June / 2026
26th / Bug Fix & Improvement
Fixed image upload issues. Replacing 'time()' function that causes path finding issues when uploading images with the Unix Converted Date as the replacement
Fixed forum image routing. Replaced 'ArchFiles' folder to 'img', the images uploaded to forum now saved inside specific forum directory inside the 'img' folder
API's now separated by it's method, example are `reauth.php` for verifying session and `getcollection.php` for retrieving collection info. For more info please see the References at the documentation
19th / MarkOut Overhaul
Reworked MarkOut UI, New detail page for MarkedOut Collection, and Ability to removed a collection from the MarkedOut
Updated styling class & Fixed download API auth check
18th / Adding API detail
API panel now include extra detail about the API in Groups management dashboard
13th / changelog created
The reason? look at this page introduction, no currently it isn't dynamically retrieved from the database but this haven't get finalized yet.
12th / the API auth and download Implemented
I've finished the API's for anyone that wanted to test the project locally or developing their own client downloader, noted that the hosting infrastruct currently used for the website doesn't support API's/non-browser processing so this functionallity aren't available on the demo site.
Api token can be obtained from API panel in your groups dashboard page.
download api does work but it currently isn't fully validated to be secure. more detail on the documentation
1st - 4th / fixing the community management tab 403 issue
The word "announce" were specifically being blocked to be used as directive and after changing the file names the site works as you might see in this changelog page you're currently visiting.
May / 2026
16th - 31st / report implementents
This is a bit of a really late realization when going to ship the project, with no way of reporting at all the community has no way of of reporting user in the forums or "malicious" publisher that published collection with malware/virus. Even though this is not permanent, I'd implement the universal report tab to be placed on forums detail, user profile, groups profile and collection detail. Each of them are gonna be proccessed possibly between 1 to 5 days depending on the case and of course this is why I required a valid email in registration, when things like this happens there will be emails to the suspected user/groups for confirmation & solution.
16th - 31st / settings & consent
It's related to privated profile info and allow groups invites. The first one was planned to added way back in Dec/2025 but forgoten until now, If it's get ticked then achivement and badge will not be shown to publics but post and currently joined groups will still be visible.
user can give consent about allowing groups sending invites and turned on by default until they joined a groups after which they must turned it on again if they wanted an invitation again.
all of this contained inside settings panel and the invitation message is shown below the settings.
16th - 31st / implemented profile picture
Yeah it's known profile picture were the most important things that should've been added a while back, priorities shifting every now and then but it is now implemented. At first I cloudn't decide whether `.gif` should be allowed or not but I figured if the size is still within limit why not just allow it. It's only get shown on profile pages anyway.
Noted this is also include the profile picture of the Groups profile pages, the groups profile picture is a must to be implemented though like the other it is also only gonna get shown on the (groups) profile pages (and the desktop app if that counts).
16th - 31st / session manager UI update
A while back(about 3 weeks ago) The old session page styling made for just the bare minimum, so I change them while borrowing UI styling from other page codes. This time the requested back button included, nothing much changes other than adding the session checker and updating the UI's as of May/11.
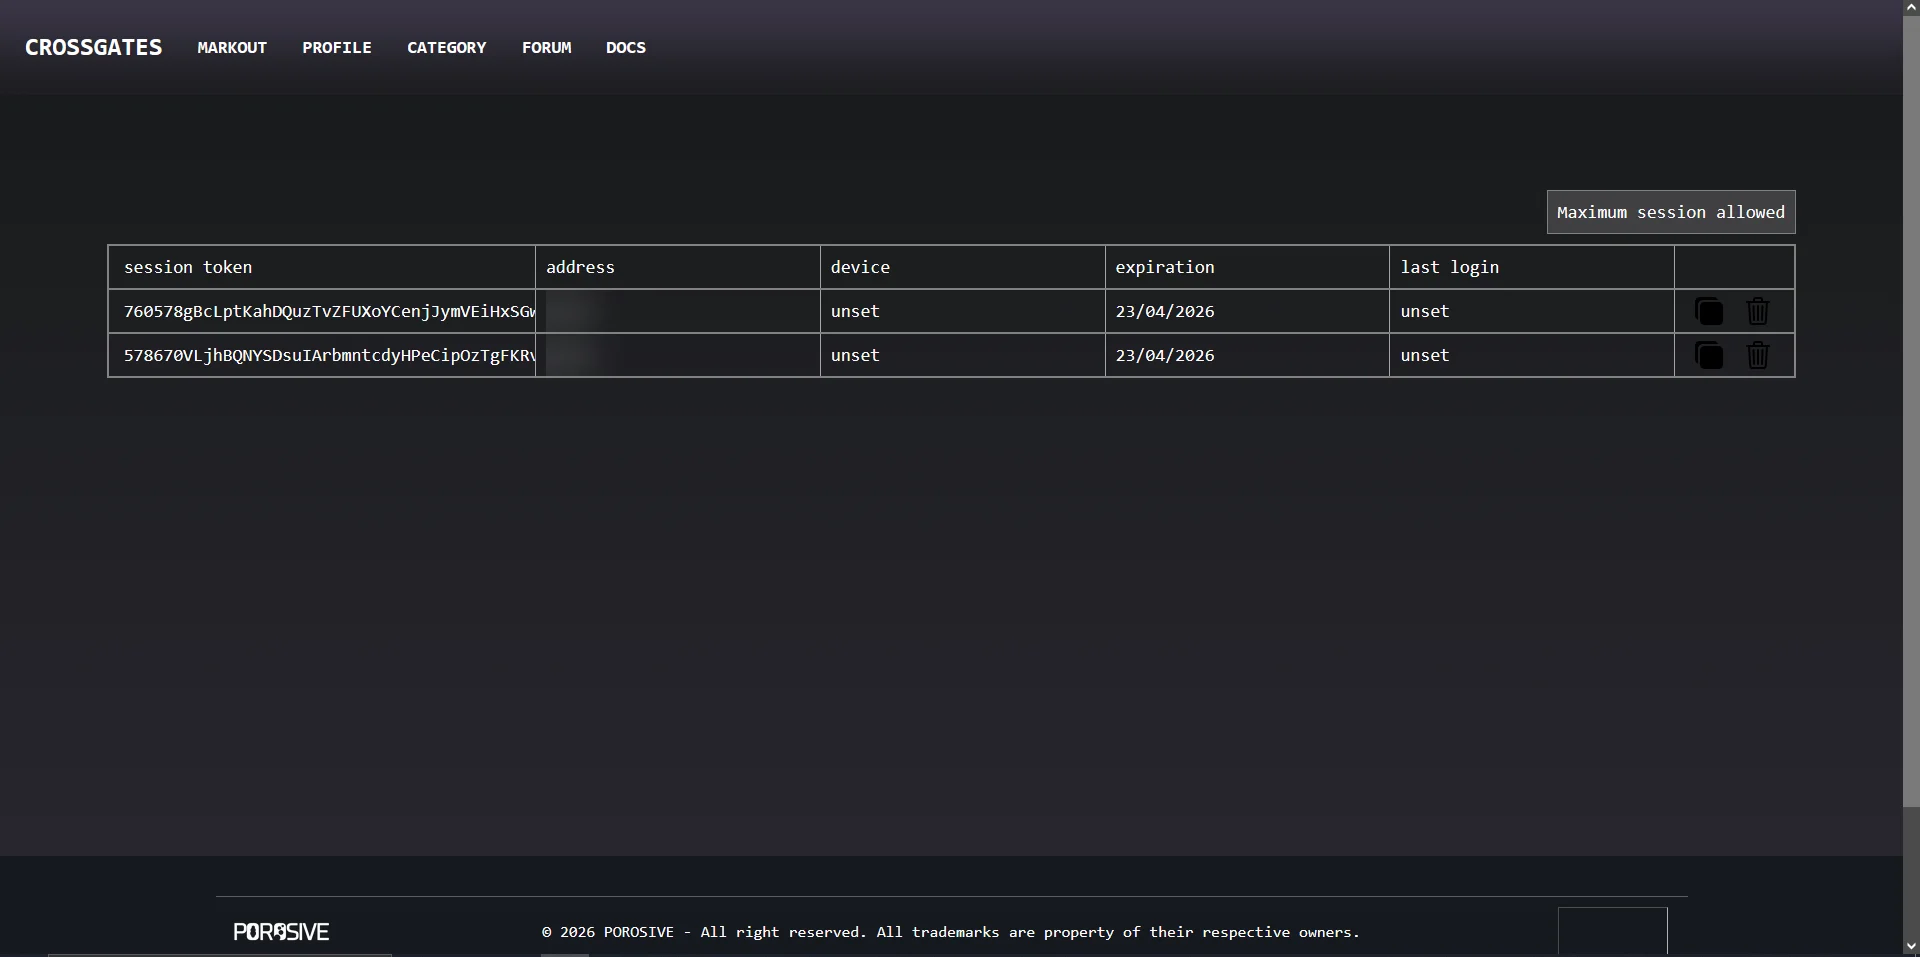
old version
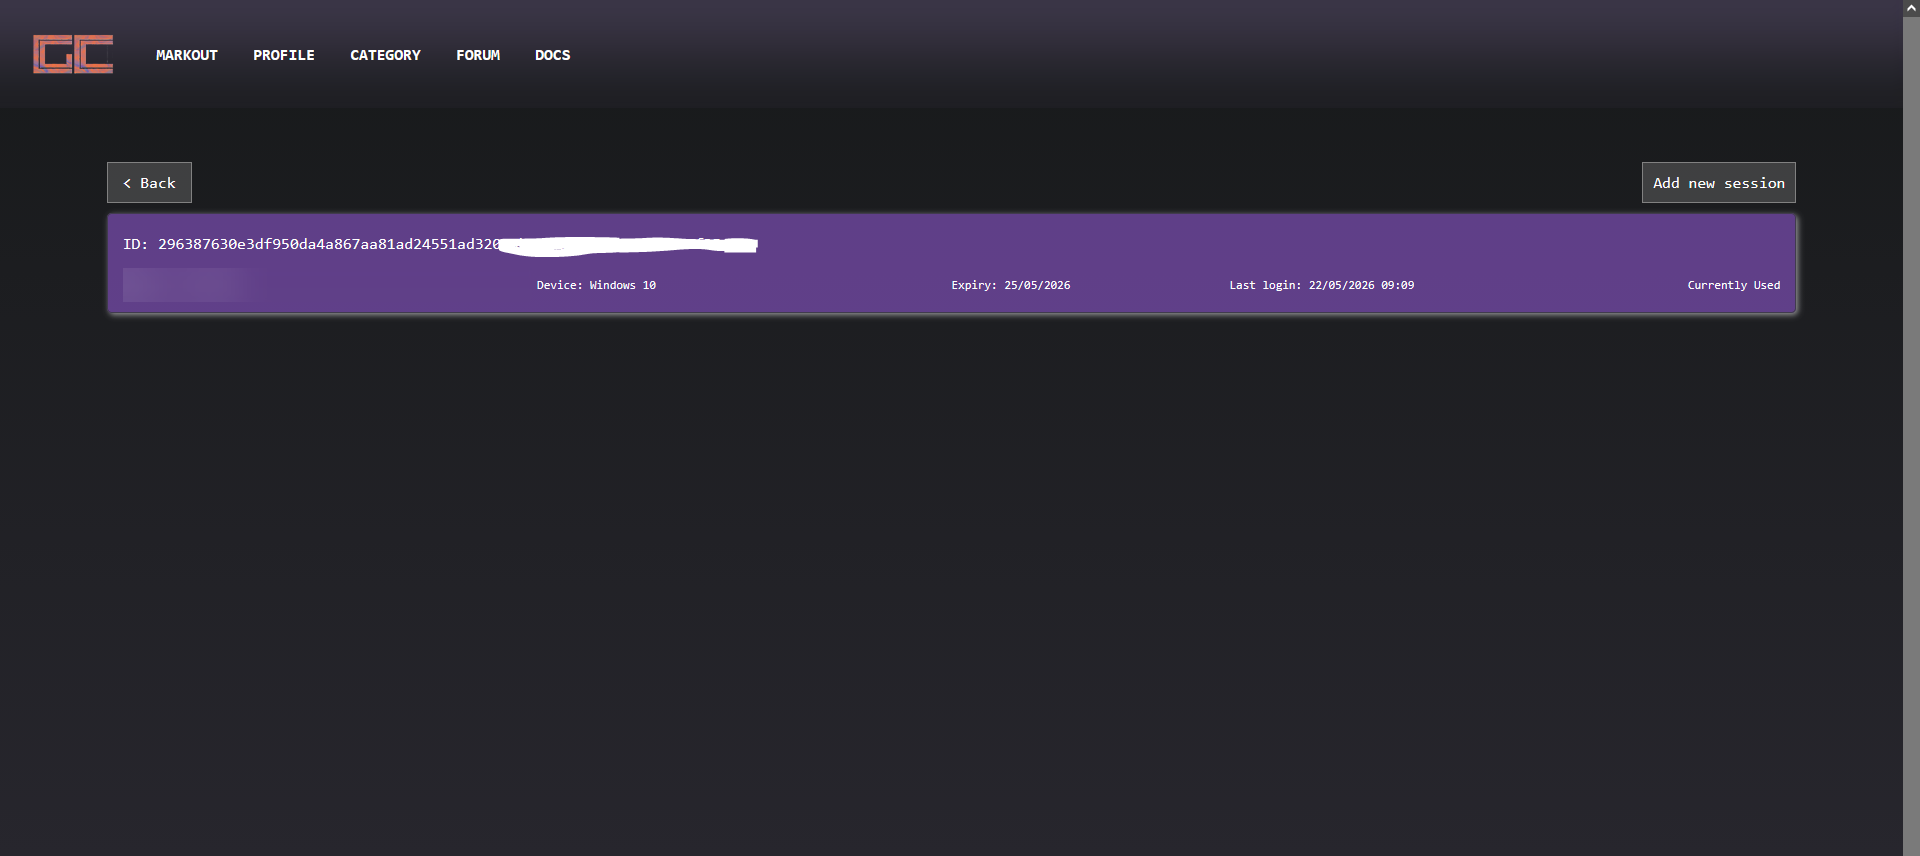
new version
16th - 31st / updated collection views
Some changes needed for help ease on the server-side, most notably external link where they're now a dynamic name and link that support up to 10 link as previously only support one website and youtube link.
It's now also support embedded video demo/trailer although it's optional and only been tested with YT video link.
16th - 31st / collection file manager
Originally this was planned for future updates the file manager is really needed in order to securely upload and update. The paranoid me really didn't want to mess up this very vunerable part of the project... here's a little breakdown of what created/removed:
- `post_file.php` were removed and replace with `file_proceed.php`, because the naming doesn't makes sense when it also does processing remove file.
- `file_manager.php` are the main pages to manage all the existing file on their vault, it will only list file that exist and will even not list phantom file written in the database. Naturally, because of the capability given to this page making this page having more layered security check just to make sure only one collection at a time allowed to be accessed by user.
- `file_proceed.php` is the one that process everything input and request from the file manager
8th - 15th / Community Management
It's a dedicated page for topics created along with the creation of collection, this is where the publisher admins/founder can post an annoucement about their collection.
8th - 15th / collection publishing
Dedicated management system to create and administer collection, originally the system can be accessed by a normal user but after the creation of the [groups-flow](#groups-flow) the publishing now can only be accessed by allowed members of a groups, this help to make sure reduce creation spamming.
- the software file and the rest of the collection creation proccessing are inevitably must be separated into `create_collection.php` and `post_file.php` because I don't believe with the real world connection speed and file upload size limit that this will be possible to be done at the same time without compromising the security, the other way this will be possible probably with the introduction of file chunking but currently I just want this to properly work
- `edit.php` handle the collection update, final publishing and archiving. Noted that it just handle the normal image and text data update where the size are still doable for the most cases
- if not obvious already, the software that will be shipped to this site must be using `.zip` format and preferably on 'store' mode. the reason were that It will took a significant amount of performance to implement separated file upload instead of this, I might implement a way to make some sort of file Ignore & replace list for the client launcher so that publisher can list which file that should/shouldn't be replaced on the client side each time an updates downloaded
7th - 15th / Invitation notification
While it is look like a notification, doesn't mean this one is a real notification system. It's function are only for notified a Groups invitation to user and nothing else, for now I'd not have plan to expand the functionality.
7th - 15th / groups-flow access system
always take a deep breath when i make something and then realizing the security missing something and this is one of them, were do I even begin..
- Invite system, now comes with nerfed and limited version of notification. of course this begin when I've got revelation that if I didn't do this, Individual can get added easily by Groups forcibly without consent.
- access login & auth, basically a more paranoid login system on steroid and auth system were making sure that every groups pages can only be accessed by identified and approved account by the groups founder.
- access system can only be created either for the founder account when a new groups created and when an invited user accepted to join the groups that invited them.
7th - 15th / groups-flow auth sessions
Groups-flow auth system were separated from the website main auth. Using more temporary session implementation though the implementation were similiar, at maximum saved for only 1 day before requiring reauthentication. this decision made because of the high security vulnerability on giving access to the groups collection and community management. And another note to when user signed in again: the old session token in database will be replaced with new ones, truthfully most auth and sessions code were reused/refactor from the main sessions code but adjusted a lot to fit the groups-flow usecase.
2nd - 15th / groups-flow
A place where developer can publish and manage their collection, within it developer can invite and manage members account, edit their public profile, create and managing collection along with making announcement about the future update to their audience. If not because of of the budget constraint and a lot of possible security issue, the Groups-Flow would operate in separate domain and database with a sync system to the main website. This might be revisited in near future if needed.
1st - 15th / session system
Thanks to the feedback from reviewer, the website now support using session token on the login system. Noted that when user are exceeding session limit but they can only use temporary session and required to tick off "keep me signed in" in order to access the website and removing unused/expired session. This alone took me a good few days to rewrite the auth and login codes